Who’s Monitoring You? Use This New Service to Discover Out – Krebs on Safety
It may be daunting to find out who’s chargeable for displaying advertisements on the web sites we go to, or who’s harvesting knowledge from the cellular apps we use every single day. That data is already semi-public, however it isn’t simply parsed and historically a lot of it has remained walled away within the palms of huge promoting platforms. Not anymore: A strong and free new service known as DecryptAds scrapes and correlates this adtech knowledge and makes it easy to rapidly be taught an important deal in regards to the entities which might be monitoring you.
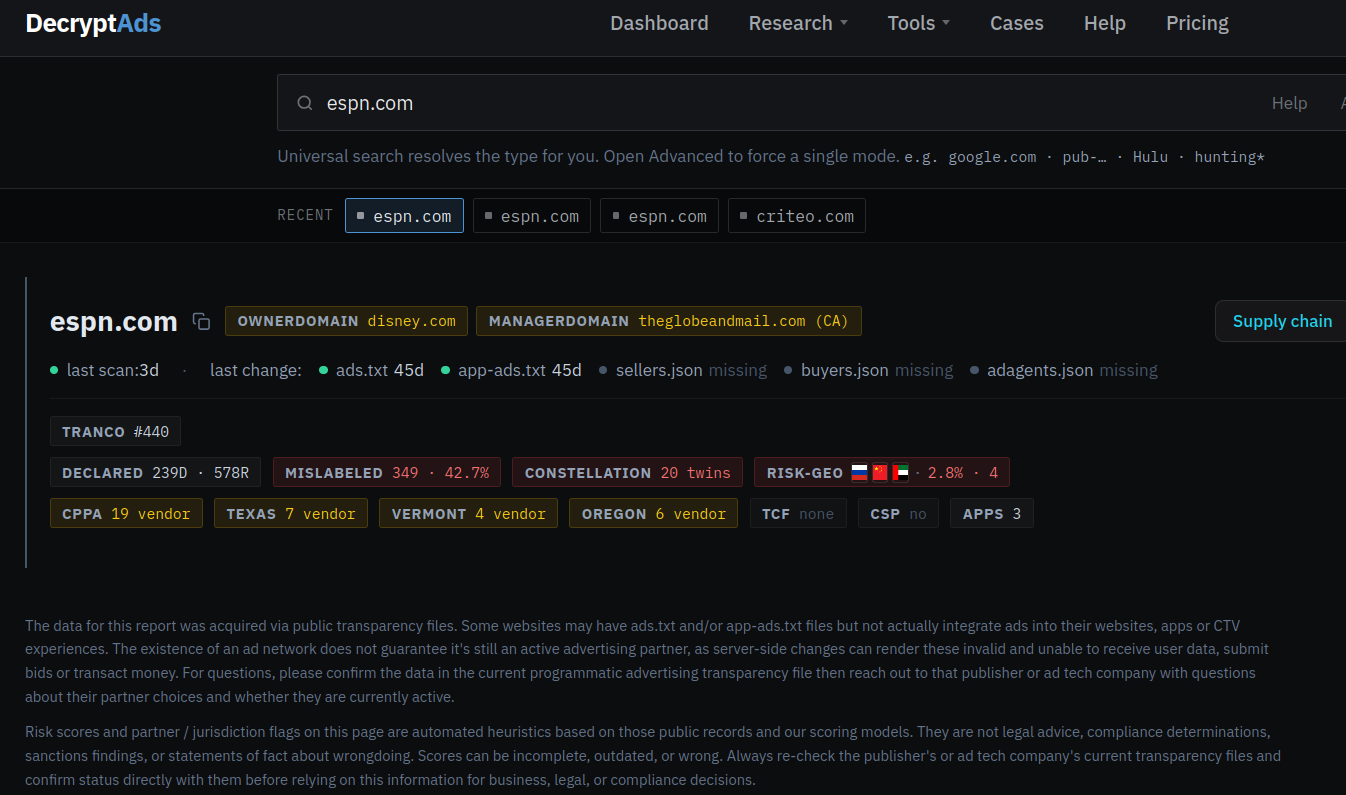
A Decryptads abstract of the promoting partnerships declared by espn.com.
The newly launched decryptads.com says it’s continuously scraping the recordsdata that web sites and apps make publicly accessible to reveal the businesses which might be permitted to run advertisements or accumulate person knowledge. These recordsdata embody:
–advertisements.txt: the entire adtech corporations and knowledge brokers that will run advertisements or harvest knowledge from the positioning;
–app-ads.txt: entities that may harvest knowledge from or show advertisements on cellular and good TV apps;
–consumers.json/sellers.json: the entities shopping for, promoting or reselling advert stock for a given web site or app.
Zach Edwards is chief analysis officer for DecryptAds and a risk researcher on the safety firm Infoblox. Edwards stated he and two different founders determined the service was wanted as a result of the adtech knowledge in these recordsdata is usually solely helpful when it may be cross-referenced to construct a extra full image of the promoting ecosystem for every web site or app.
“It’s an adtech software however we’re making an attempt to strategy adtech from a safety perspective,” Edwards stated. “It’s actually constructed for lots of privateness and safety use instances which have been dramatically underserved.”
These use instances, he stated, embody monitoring down the supply of malicious advertisements that attempt to foist malware on focused customers, figuring out advert networks situated in adversarial nations, and detecting the quick rising swarms of AI-generated slop web sites and apps. And as decryptads.com demonstrates, these potential safety and privateness threats are close to unimaginable to detect simply by viewing a single apps.txt or app-ads.txt file.
“Provide-chain integrity points not often stay in a single file,” the positioning explains. “They present up as damaged cross-references between advertisements.txt, app-ads.txt, and sellers.json recordsdata; as cloned declaration units throughout unrelated domains; as vendor removals that solely make sense when seen throughout exchanges; and at the same time as provide paths in bid logs that by no means truly seem in any given writer’s authorized-seller listing.”
A search in DecryptAds for the vastly in style sports activities community espn.com reveals 143 advert companions and 19 registered knowledge dealer domains are listed inside its ads.txt and app-ads.txt recordsdata. That knowledge dealer data is regularly turning into accessible as a result of 4 states — California, Oregon, Texas and Vermont — have lately handed legal guidelines requiring knowledge brokers to register in the event that they purchase or promote knowledge on customers from these states. DecryptAds experiences that just about half of these knowledge brokers are accumulating geolocation knowledge from espn.com guests who aren’t blocking advertisements, whereas one other three disclose that they accumulate gadget fingerprints and delicate private data.

A visible illustration of the complicated advert provide chain declared by espn.com. Picture: decryptads.com.
HIGH-RISK AD PARTNERS
DecryptAds additionally makes it simple to be taught the beneficiaries and nationwide origins of the promoting companies lurking in apps and web sites, displaying a conspicuous warning when adtech companions of an app or web site are based mostly in “geo-risk” areas like China and Russia, or in nations with robust monetary and political ties to each — corresponding to Cyprus and the United Arab Emirates (UAE).
In accordance with DecryptAds, espn.com works with 4 completely different promoting entities which might be based mostly in both Russia, China or the UAE, together with the adtech agency Between Digital, which lists a New York deal with. Nonetheless, the dossier on Between Digital flags them as a Russian agency, displaying that their publisher offers (PDF) are processed via Alfa Financial institution, Russia’s largest non-public business financial institution and one in all a number of monetary establishments positioned below U.S. sanctions in 2022 after Russia invaded Ukraine. KrebsOnSecurity sought remark from each Between Digital and the corporate’s founder, and can replace this story within the occasion that both replies.
A seek for a number of prime U.S. army information web sites — together with armytimes.com, airforcetimes.com, defensenews.com, navytimes.com, marinecorpstimes.com and federaltimes.com — reveals all of them enable Between Digital to serve advertisements and monitor customers, in addition to two entities within the UAE and one other within the possession secrecy haven of Panama. DecryptAds experiences that Between Digital is accumulating advert knowledge on roughly 55,000 accomplice web sites.

The “Geo Danger” part of decryptads.com.
Pivoting on Between Digital’s app-ads.txt file reveals a whole bunch of domains that includes easy web-based video games which might be incessantly interrupted by advertisements. Edwards stated Between Digital’s personal declarations present the corporate is listed as each a writer and a reseller on roughly two-thirds of their portfolio.
“It means they’re mainly enjoying either side of the bidding equation, which creates alternatives to direct consumer spend at your owned and operated properties or consumer infrastructure, basically creating alternatives for conflicts of curiosity,” Edwards instructed KrebsOnSecurity. “The issue we now have proper now could be that for years we’ve had virtually nobody policing these advertisements.txt and app-ads.txt recordsdata.”
The Opera Net browser stays fairly in style, and doubtless many customers are unaware that since 2016 it has been majority owned and managed by the Chinese language firm Kunlun Tech (the operational headquarters of Opera stay in Oslo, Norway).
Opera.com’s profile at DecryptAds identifies 27 registered knowledge brokers accumulating data, together with 15 adtech companions within the UAE, six in China, three in Cyprus, two in Russia and one every in Hong Kong and Ukraine. DecryptAds makes clear, nonetheless, that these corporations symbolize simply seven % of the adtech companions laid out in Opera.com’s advertisements.txt and app-ads.txt recordsdata.
LEGAL DOSSIERS
One function of DecryptAds that despatched this creator down a number of hours-long analysis rabbit holes is its Legal Dossier lookup, which takes a number of minutes for every search however ultimately churns out oodles of helpful details about who owns a selected area or app, when it was registered, and any aliases or relationships it might need to adtech corporations and different web sites or apps.
For instance, final month KrebsOnSecurity wrote about researchers from Bitsight who discovered that a particularly in style line of TV streaming sticks known as H96 quietly lease out every person’s Web connection to strangers. Bitsight additionally found that when these gadgets aren’t getting used to stream pirated video content material, they are spoofing themselves as mobile phones clicking ads on AI-generated slop websites.
Bitsight concluded that the identical Chinese language firm that made a number of of the malicious apps widespread to all of those H96 streaming sticks — the Fengwo Group — additionally additionally ran the community of advertisements and AI slop web sites being clicked on by tens of 1000’s of those gadgets which might be pretending to be cell phones.

Examples of advert touchdown pages linked to the Fengwo Group. These websites had been designed to indicate advertisements solely to H96 gadgets that had been spoofing their gadget kind as cell phones. Picture: Bitsight.
A DecryptAds authorized file on the (now dormant) Fengwo Group area title for the AI slop web site pictured on the left within the screenshot above (medicalbeautyhub dot com) reveals it shares a vendor ID (1674071) with a gaming web site — giacoloredstones[.]com — which options yet one more vendor ID (103488000).
Pivoting on that latter vendor ID reveals a whole bunch of lively web sites inside Russia’s Yandex advert system that includes extraordinarily low-quality video games or easy utilities that pepper guests with advertisements.
QUIET REMOVALS
Edwards stated that when promoting networks suspect a given advertiser is engaged in unauthentic clicks or displaying malicious advertisements, fairly often these networks will quietly take away the offender from their listing of authorized companions with out letting anybody else learn about their suspicions.
This apply, he stated, makes it simpler for dodgy adtech companies to keep away from accountability and proceed victimizing others. To handle that visibility hole, DecryptAds contains a quiet removals feed that data and correlates the entire sellers.json removals throughout advert exchanges for a similar vendor area or title.

A screenshot of the Quiet Removals Feed at decryptads.com.
“The best way the adtech business works, somebody will write a report about advert fraud and solely share it with their very own purchasers they usually received’t make it public,” Edwards stated. “The ban is simply eradicating them from the sellers.json file, however they instructed no person. At some point it was there, the subsequent it was gone. So should you’re making an attempt to navigate who’s suspicious, that’s often powerful to do as a result of there are numerous adtech corporations eradicating issues unexpectedly.”
MALVERTISING AND AI SLOP
Malvertising, the time period given to the apply of inserting malicious advertisements that foist malware or redirect guests to phishing pages, stays an all-too-frequent prevalence within the fashionable adtech business. However Edwards stated these malicious advertisements are way more generally discovered now on newly generated AI slop web sites than on excessive site visitors locations that sometimes make use of quite a lot of applied sciences and third get together instruments to rapidly flag dangerous advertisements.
“None of those slop AI content material farms are paying for that form of safety,” he stated. “They’re simply signing up the bottom high quality companions, and it basically turns into a greased rail to focus on the customers of these websites with malicious advertisements. Most malvertising assaults don’t occur on espn.com or huffpost.com, however quite [on] some decrease high quality content material farm and somebody simply went there as a result of it got here up in a search.”
Edwards stated the AI slop web sites are populated with machine-generated weblog posts and pictures, and canopy a big selection of themes from dwelling enchancment and adorning to meals recipes, searching, automobiles and shopper expertise. He stated organizations that get hit with malicious advertisements are sometimes at a loss for what to do subsequent, unaware that most often the reply is likely one of the entities listed inside the web site’s advertisements.txt or app-ads.txt file.
“Loads of critical organizations are beginning to perceive that if we’re not breaking down this advert knowledge, we’re not going to know who’s focusing on authorities folks with zero-click payloads on an virtually each day foundation,” he stated.
Edwards maintains that really getting a deal with on the malvertising and AI slop issues would require extra data-sharing by the key advert networks. Particularly, he says these platforms don’t broadly share what’s often called the “provide chain object” or SCO, structured knowledge connected to every promoting bid request that lets consumers see each vendor, reseller and middleman concerned in passing an advert impression from the writer to the ultimate purchaser.
“That SCO tells you who offered it or resold it, and who was the ultimate entity that purchased the impression that served that malware payload,” Edwards defined. “You might even see the malicious zero-click redirection, however with out the provision chain object — which is just served server facet — you received’t know who focused your folks with malware and received’t have a technique to attempt to forestall it correctly. But when we are able to encourage the adtech business to show that SCO, it’ll get simpler to seek out the wrongdoer behind anybody dangerous advert.”
DecryptAds additionally affords an utility programming interface (API) that permits researchers to automate queries and combine the positioning’s performance into in style AI platforms.
WHAT CAN YOU DO?
The one sane response to the examples described above is to dam all on-line advertisements outright. This strategy is broadly endorsed by safety specialists as a result of it additionally makes it harder for adtech companies and knowledge brokers to construct detailed profiles on you and monitor your actions across the net and in the true world.
Nonetheless, a lot is determined by the way you usually desire to browse the Web, and the way a lot belief you place in third get together browser plugins and extensions. For these primarily browsing through a daily desktop or laptop computer Net browser, uBlock Origin Lite is a wonderful free and well-maintained open supply possibility. uBlock Origin additionally ought to work with cellular browsers like Firefox, however apparently solely on Android-based gadgets.
Adblock Plus is an honest possibility for iPhone and iPad customers. For energy customers, Adblock and uBlock Origin each help customized blocking guidelines from easylist.to, which publishes a incessantly up to date listing that removes most ads from webpages.
The properly established browser extension NoScript blocks all non-approved Javascript code, and it usually does a advantageous job blocking most advertisements from loading. Nonetheless, script blockers like NoScript might not be appropriate for common customers who don’t take pleasure in continuously having to referee which scripts needs to be allowed to load so that every web site shows correctly.
Extra technically inclined/adventuresome readers ought to strongly think about a {hardware} strategy to blocking advertisements on the native community stage, as a result of that’s simply the most cost effective, most safe and scalable technique to do it. A tiny, low-cost and broadly accessible laptop often called a Raspberry Pi might be changed into a powerful ad blocker for all devices on a local network when fitted with a microSD reminiscence card and a free program known as Pi-hole. When you’ve set it up correctly and adjusted your router’s community settings to make use of the Pi-hole’s DNS sinkhole and DHCP servers, it ought to forestall advertisements from displaying on any gadgets linked to that community.
Keep in mind that advert blockers usually do little to dam advertisements and/or monitoring that happens from inside cellular apps that customers have chosen to put in on their gadgets. Many web sites now push customers to put in a cellular app, supposedly with a view to extra totally entry and benefit from the web site’s providers and content material. However in my expertise, they’re not doing this as a result of the person expertise is in some way manner higher on the app (as LinkedIn tries to persuade us non-app customers a number of occasions per week through e-mail). Quite the opposite, I discover most cellular apps to be horribly designed, annoying, and/or fully pointless, and when given the choice I’ll virtually all the time select to work together with a web site or service instantly in a Net browser.
No, the chilly reality is that large net locations are inclined to get pushy with their apps as a result of they make it simpler for these corporations to maintain you on their platforms longer and to gather (and in lots of instances resell) far more precise data about who, what and the place their customers are. Additionally, corporations pushing prospects the toughest to put in cellular apps all the time appear to liberally choose everybody in to having their knowledge used to coach giant language fashions as of late. So be cautious in regards to the apps you put in in your cellular gadgets (including any smart TVs!), and poke round their listings at DecryptAds if you wish to be taught extra about their privateness practices and any relationships they could need to adtech companies.
Source link